DevOps methodologies have changed the way tech companies build and ship software. They’ve also introduced a growing layer of infrastructure complexity that never goes away; it compounds. While it’s possible to manage that complexity manually, it costs enormous time and headcount, and it’s not a one-time investment.
DevOps automation allows organizations to force-multiply their existing engineering teams, which is why Infrastructure as Code tools have become standard practice. The IaC landscape has also shifted dramatically: licenses have changed, platforms have added AI-native capabilities, and some tools have been deprecated entirely. Here’s a look at 10 of the best IaC tools across multi-cloud and platform-specific purposes, so your team can make an informed decision.
Benefits of Infrastructure as Code Tools
If your team is evaluating IaC tools for the first time, or re-evaluating your current stack, here are the core benefits to keep front of mind:
Speed
Instead of spending months building the infrastructure foundation before shipping your first feature, the right IaC platform lets you hit the ground running. The best platforms now accelerate this further with AI-driven automation that handles provisioning, deployment, and incident response without manual intervention.
Security and Compliance
Moving fast doesn’t have to mean moving carelessly. The best IaC platforms now provision security controls, compliance frameworks (SOC 2, HIPAA, PCI-DSS, FedRAMP), and audit trails out of the box, so your team isn’t bolting on compliance after the fact.
Flexibility
Modern IaC tools support multi-cloud environments, hybrid setups, and a wide range of integrations. The best platforms grow with your team, whether you’re at five engineers or fifty, without requiring a DevOps hire at every new stage of growth.
AI-Augmented Automation
The defining differentiator between IaC platforms today is their depth of AI integration. Platforms are moving from “write less code” to “write almost no code at all,” with AI agents that can execute, govern, and optimize cloud infrastructure autonomously within defined guardrails.
Now a baseline requirement
Support
When a critical deployment breaks at 2am, you want a dedicated support structure, not a community forum thread from 2019. Enterprise-grade IaC platforms back their software with SLAs, dedicated support teams, and increasingly, AI-powered help desks that can triage and resolve issues in real time.
Quick Comparison: 10 IaC Tools at a Glance
| Tool | Cloud Support | AI Features | Best For |
|---|---|---|---|
| DuploCloud | AWS, Azure, GCP + on-prem | ✅ AI DevOps Engineers, multiplayer agents | Overloaded DevOps teams, compliance-heavy orgs |
| Ansible (Red Hat) | Multi-cloud | ✅ AI automation orchestrator, MCP integration | Agentless automation, existing Red Hat shops |
| Progress Chef | Multi-cloud + on-prem | ⚠️ Limited | Enterprise config management at scale |
| Puppet | Multi-cloud + on-prem | ✅ AI Infra Assistant (GPT-5 powered) | Large server fleets, enterprise IT |
| Pulumi | Multi-cloud (160+ providers) | ✅ Pulumi Neo agent, Pulumi Copilot | Developer-first teams, Terraform migration |
| Spacelift | Multi-cloud (via Terraform, Pulumi, etc.) | ✅ Spacelift Intent (natural language) | Platform teams managing multiple IaC tools |
| Terraform / OpenTofu | Multi-cloud (3,000+ providers) | ⚠️ Limited natively | Teams with existing HCL investment |
| AWS CloudFormation | AWS only | ⚠️ Via AWS integrations | AWS-only shops, SAM serverless workloads |
| Azure Bicep | Azure only | ✅ MCP server tools, snapshot diffs | Azure-first organizations |
| GCP Infra Manager | GCP only | ⚠️ Limited | GCP-first teams migrating from Deployment Manager |
Multi-Environment IaC Tools
Most of the leading Infrastructure as Code tools today are cloud-agnostic, designed to manage infrastructure across AWS, Azure, GCP, and on-premises environments simultaneously. Here are the seven most important multi-environment tools available today.
1. DuploCloud
DuploCloud has evolved well beyond its roots as a no-code/low-code DevOps tool. The platform now combines two components working together:
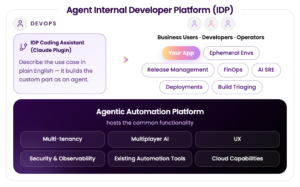
1 Agentic Automation Platform
Pre-built by former DevOps engineers, this layer handles approximately 70% of DevOps work that’s common across every engineering team — pipeline execution, Kubernetes deployments, log fetching, just-in-time access, compliance checks, and patching. It integrates with your existing toolchain (Jenkins, Argo, and others) via API or MCP, so you’re not ripping anything out.
Pre-built, standardized, already done
2 AI Coding Assistant
For the remaining 20–30% of work that’s unique to your team, DuploCloud’s AI Coding Assistant scans your platform, builds only the custom logic you need, and deploys it as a live agent. You define the input, output, and workflow. The platform does the rest.
Custom work, built fast
DuploCloud recently launched AI DevOps Engineers, an agentic service that can provision, troubleshoot, and optimize infrastructure within defined guardrails. The platform’s Agentic Help Desk gives teams a conversational interface to triage tickets, trigger deployments, and resolve incidents. Multiplayer AI agents support Claude, OpenAI, Gemini, and open-source models, all swappable per workflow by administrators.
On compliance, DuploCloud remains one of the deepest solutions on the market, with native support for SOC 2, HIPAA, PCI-DSS, GDPR, FedRAMP, and HITRUST baked into its SecOps workflows from day one. Developers can provision cloud-native infrastructure across AWS, Azure, and GCP, including hybrid-cloud setups with Kubernetes on-prem.
Best for: Engineering teams with 3+ DevOps engineers drowning in repetitive work, first DevOps hires at well-funded startups that need the leverage of a full team, and platform engineering leads building an internal developer platform who want the foundation pre-built.
2. Ansible (Red Hat Ansible Automation Platform)
Ansible is an open-source cloud orchestration and configuration management tool designed by Red Hat. Today it’s available both as the open-source Ansible project and as the enterprise-grade Red Hat Ansible Automation Platform. The gap between those two has grown substantially.
Ansible’s core approach remains the same: configuration models called Playbooks, written in a YAML-based DSL, define your infrastructure and automation logic. Once established, Playbooks make it fast to create consistent environments with security and compliance protocols already in place. A vast library of pre-configured community modules covers virtually every common use case, and custom configurations are fully supported.
Red Hat announced major AI-driven innovations to the Ansible Automation Platform at Red Hat Summit, positioning the platform as the “trusted execution layer for IT operations in an agentic era.” Ansible Automation Platform 2.7 (GA June 2026) shipped a native MCP server integration in technology preview, enabling AI agents to query jobs, gather facts, and launch automation workflows through natural language. The platform also added an expanded automation portal with a visual execution environment builder and an enhanced AI assistant that supports bring-your-own-knowledge for enterprise-specific guidance.
Best for: Organizations already in the Red Hat ecosystem, teams that need agentless automation across heterogeneous environments, and enterprise IT shops managing large-scale configuration at scale.
3. Progress Chef
Progress Chef has been helping developers manage server-based deployments for nearly 20 years. Its central premise of repeatable system configuration “recipes” that ensure consistent results across environments remains sound. Chef’s approach to hardened infrastructure testing, deployment, and validation still resonates with enterprise teams managing complex, compliance-heavy server fleets.
The product portfolio has now consolidated around the Chef 360 Platform, which provides a unified pane of glass for fleet-wide visibility and control across configuration management, application delivery, edge/device management, and security compliance. Chef Client 19 (latest: 19.3.15 as of May 2026) introduces Hab-based builds for more consistent cross-environment builds. The cloud security and CSPM capabilities continue to help teams maintain compliance across cloud-native assets.
Best for: Enterprise organizations with existing Chef investments and complex on-premises or hybrid server fleets. Teams considering Chef for new projects should evaluate whether the open-source deprecation path aligns with their planning horizon.
4. Puppet
Puppet is a declarative Infrastructure as Code tool built for organizations managing multiple application servers simultaneously. Its Ruby-based DSL lets users describe the desired end state of their infrastructure, and Puppet handles figuring out the best path to get there. Pre-configured modules and multi-cloud automation supporting all major platforms remain core to the offering.
Puppet has been steadily modernizing. Puppet Enterprise 2025.11 ships with an updated Infra Assistant now powered by GPT-5 series models, improving response quality, reasoning, and PQL generation for infrastructure queries. July 2026 brought significant module updates including broader Windows Server 2025 support and expanded Continuous Delivery tooling. Puppet Core 9 is on the near-term roadmap, and the company is shifting to a new ‘Latest’ and ‘Latest -1’ support lifecycle model starting with the next major PE release (projected August 2026).
Best for: Enterprises with large, heterogeneous server fleets that have standardized on declarative infrastructure management over many years and want AI-assisted querying and automation layered on top of that foundation.
5. Pulumi
Pulumi is an open-source Infrastructure as Code platform that lets developers define infrastructure in the programming languages they already know: TypeScript, Python, Go, Java, C#, and more, complete with IDE autocomplete, type checking, and native testing frameworks. No YAML or HCL required.
Pulumi has made some of its most significant product moves to date. The platform launched Pulumi Neo, an autonomous AI agent that can execute, govern, and optimize complex cloud automations by understanding resource dependencies, enforcing policies, and keeping human operators in the loop at defined checkpoints. Pulumi Copilot adds a conversational layer that lets teams query the state of any resource managed by Pulumi in plain language.
In a major strategic shift, Pulumi Cloud now manages Terraform and OpenTofu workflows alongside native Pulumi IaC, and Pulumi IaC itself now speaks HCL. This means teams can migrate gradually from Terraform to Pulumi without a big-bang rewrite. Pulumi’s Azure Native V3 delivered a 75% reduction in SDK size while maintaining complete Azure ecosystem coverage. With 160+ cloud providers supported, Pulumi is one of the broadest multi-cloud IaC platforms available.
Best for: Developer-centric teams who want IaC in familiar programming languages, organizations migrating from Terraform looking for a modern alternative, and platform engineers who want AI-native cloud automation with strong policy enforcement.
6. Spacelift
Spacelift is an IaC orchestration platform purpose-built to unify and govern multiple Infrastructure as Code tools under a single control plane. Rather than replacing your IaC tooling, Spacelift sits on top of it, adding shared policy, drift detection, pull request integrations, real-time approvals, and self-service infrastructure across Terraform, OpenTofu, Pulumi, CloudFormation, Ansible, Kubernetes, and Crossplane.
Spacelift has repositioned itself as an AI-native infrastructure orchestration platform. Analysts have described this shift as moving from IaC management to “Infrastructure-as-Context,” where the platform understands your infrastructure semantically rather than just as code files. The flagship AI feature is Spacelift Intent, which can deploy modules from your registry using plain-language descriptions. Spacelift Flows (now GA) brings IaC-style rigor to Day 2 operations like scaling, patching, and incident response. The Templates feature lets platform teams define guardrails while giving developers the self-service experience they need.
Best for: Platform engineering teams managing distributed engineering organizations across multiple IaC tools, geographies, and specialties, especially those who need policy, drift detection, and self-service infrastructure in one place without dictating what IaC tool every team uses.
7. Terraform / OpenTofu
Terraform remains one of the most widely adopted IaC tools in the world, with a declarative HCL syntax and a provider ecosystem spanning 3,000+ integrations. Its ability to manage hybrid and multi-cloud environments with consistent workflows has made it a common underpinning of cloud architectures, and that foundation isn’t going anywhere for teams already invested in it.
But the licensing and ownership landscape has changed the calculus for new adoptions. The BSL restricts use of Terraform “in a competitive way” against HashiCorp/IBM products, and IBM’s 2025 acquisition raised fresh questions about long-term stewardship and roadmap independence.
Enter OpenTofu. The open-source Terraform fork, maintained by the Linux Foundation and CNCF, has matured into a credible drop-in replacement. As of June 2026, OpenTofu v1.12.2 is the current stable release, with over 29,000 GitHub stars and 70+ active contributors. OpenTofu has shipped features that have never landed in upstream Terraform, including state encryption (v1.7), provider for_each (v1.9), early variable evaluation in backend configuration (v1.8), and the -exclude flag (v1.9). The Cloud Development Kit for Terraform (CDKTF) remains available for teams who prefer TypeScript, Python, Java, C#, or Go.
Best for: Teams with existing Terraform codebases and HCL investment. For new projects, OpenTofu is worth evaluating as the open-source alternative, particularly for organizations that want to avoid BSL licensing ambiguity. Pulumi Cloud can now also manage Terraform/OpenTofu workflows for teams considering a longer-term migration path.
Platform-Specific IaC Tools
If your organization runs on a single cloud provider, the native IaC tools from each major platform offer deep integration, zero additional cost, and first-party support for every service as it launches. Here are the three most important platform-specific options, including one significant deprecation to be aware of.
8. AWS CloudFormation
AWS CloudFormation is a declarative IaC platform for provisioning and managing AWS resources. Automation templates written in YAML or JSON can be parameterized, versioned, and deployed consistently across any AWS account or region. Core capabilities include pre-deployment change set previews, rollback triggers that revert code to its previous state on errors, and deep integration with AWS governance controls and IAM.
Recent updates include EC2 Auto Scaling now supporting Instance Refresh as a native CloudFormation update policy, enabling controlled, alarm-monitored rolling updates with launch-before-terminate logic and configurable bake times. AWS also updated the SAM CLI with expanded CloudFormation integration, improving infrastructure-as-code workflows for serverless applications and streamlining local testing. CloudFormation continues to expand resource coverage as new AWS services launch.
Best for: AWS-native organizations that want zero-cost IaC tightly integrated with AWS governance, IAM, and service launches. Teams with significant multi-cloud requirements, or those needing AI-driven automation beyond CloudFormation’s scope, should evaluate tools like Pulumi or DuploCloud alongside it.
9. Azure Bicep
Azure Bicep is Microsoft’s domain-specific language for Azure Infrastructure as Code, and it has fully replaced ARM JSON as the recommended authoring experience. Bicep offers cleaner, more readable syntax while maintaining complete parity with ARM Templates under the hood. Every Azure service and API version available in ARM is available in Bicep on day one.
Bicep has expanded well beyond core Azure resources. It now supports Microsoft Entra ID, Microsoft 365 resources, and OS-level configurations via DSC (Desired State Configuration). The bicep snapshot command reached general availability in v0.41.2, generating normalized snapshots of resources that can be stored and compared across deployments, making infrastructure review workflows substantially more tractable. New MCP server tools have also been added for Bicep, including file diagnostics, decompilation of ARM templates, and deployment snapshot retrieval, enabling AI assistant workflows around infrastructure review and drift detection.
Best for: Azure-first organizations starting new infrastructure projects. Teams with existing ARM JSON templates can maintain them as-is; Bicep’s decompile tooling can help convert them over time.
10. Google Cloud Infrastructure Manager
Google Cloud Infrastructure Manager (Infra Manager) is Google’s replacement for Cloud Deployment Manager, and it takes a fundamentally different approach. Where Deployment Manager used YAML-based configurations and Jinja/Python templates, Infra Manager uses Terraform as its core IaC language, giving GCP-native teams access to the broader Terraform provider ecosystem alongside Google’s managed service wrapper.
Infra Manager provisions and manages Google Cloud resources using Terraform configurations stored in Cloud Source Repositories or Cloud Storage, with full integration into IAM, Cloud Audit Logs, and the GCP console. Google provides a DM Convert tool to help teams migrate existing Deployment Manager configurations to the Infra Manager format. Because it’s Terraform-backed, GCP teams using Infrastructure Manager can also benefit from the broader Terraform and OpenTofu tooling ecosystem, including Spacelift, Pulumi’s Terraform support, and existing HCL module libraries.
Best for: GCP-first organizations managing their infrastructure as code. Teams previously on Cloud Deployment Manager should prioritize migration. Google’s DM Convert tooling makes this tractable, but the June 30, 2026 new-user block means the deprecation clock is running.
Choosing the Right IaC Tool in 2026
The right IaC tool depends on your cloud environment, team size, compliance requirements, and how much of your infrastructure work you want to automate. Platform-specific tools (CloudFormation, Bicep, Infra Manager) win on tight integration and zero cost when you’re all-in on one cloud. General-purpose tools (Terraform/OpenTofu, Pulumi, Ansible) win on flexibility and breadth. Orchestration layers (Spacelift) win when you’re managing multiple IaC tools and teams. Configuration management platforms (Chef, Puppet) win on large-scale server fleet management.
And then there’s a different category entirely: platforms like DuploCloud that take the question of IaC tool selection largely off the table by automating the infrastructure work itself, not just the code to describe it.
Whether you’re a three-person DevOps team drowning in repetitive work, a first DevOps hire at a well-funded startup, or a platform engineering lead building an internal developer platform, get in touch with DuploCloud to see how much of your current infrastructure workload can be handed off to an agent.
FAQs
What is Infrastructure as Code (IaC)?
Infrastructure as Code is the practice of managing and provisioning computing infrastructure through machine-readable configuration files rather than manual processes or interactive configuration tools. IaC allows teams to version, test, and replicate infrastructure the same way they manage application code, enabling faster deployments, fewer configuration errors, and consistent environments across development, staging, and production.
What’s the difference between Terraform and OpenTofu?
Terraform is now maintained by IBM (which acquired HashiCorp in 2025) under the Business Source License (BSL), which restricts competitive use. OpenTofu is an open-source fork of the last MPL-licensed version of Terraform, maintained by the Linux Foundation and CNCF. Both use HCL syntax and are largely compatible, but OpenTofu has shipped several features (state encryption, provider for_each, early variable evaluation) that have not landed in upstream Terraform. For new projects, teams should evaluate whether Terraform’s BSL licensing is a concern for their use case.
Is Google Cloud Deployment Manager still supported?
No. Google Cloud Deployment Manager reached end of support on March 31, 2026. As of June 30, 2026, new users are blocked from enabling the Deployment Manager API. Google’s recommended replacement is Infrastructure Manager, which uses Terraform as its underlying IaC language. Google provides a DM Convert tool to help teams migrate existing Deployment Manager configurations.
How is AI changing IaC tools?
Every major IaC platform has added AI capabilities recently, but the depth varies significantly. Some tools (Puppet, Ansible) have added AI assistants for querying and generating automation. Others (Pulumi, Spacelift) have added autonomous agents that can execute deployments and Day 2 operations. DuploCloud has gone furthest, with AI DevOps Engineers that handle provisioning, troubleshooting, and optimization as a managed service within defined guardrails, across the full infrastructure lifecycle.
Which IaC tool is best for compliance-heavy workloads (HIPAA, SOC 2, FedRAMP)?
DuploCloud is the strongest option for teams with significant compliance requirements. It provisions SOC 2, HIPAA, PCI-DSS, GDPR, FedRAMP, and HITRUST controls natively as part of its infrastructure automation, not as an add-on. General-purpose IaC tools like Terraform or Pulumi can support compliance workflows, but require significant custom policy work (using tools like OPA, Sentinel, or Checkov) to achieve equivalent coverage. For teams where compliance is a core requirement rather than an afterthought, DuploCloud’s built-in approach is considerably faster to production.
What is the difference between configuration management tools (Ansible, Chef, Puppet) and IaC provisioning tools (Terraform, Pulumi)?
Provisioning tools like Terraform and Pulumi are designed to create and manage the infrastructure itself — virtual machines, networking, storage, Kubernetes clusters, cloud services. Configuration management tools like Ansible, Chef, and Puppet are designed to configure what runs on that infrastructure — installing software, managing users, applying security policies, and keeping systems in a desired state. In practice, the lines have blurred significantly: Ansible can provision cloud resources, and Terraform can trigger configuration scripts. Many mature DevOps stacks use both categories together.